Focused assessment
We define the target and testing period, then document confirmed vulnerabilities in an assessment report.
Penetration testing
Layer8's AI and security engineers assess web applications and APIs for paths that could lead to unauthorized access or actions. Before testing, we agree on the scope and operating conditions. The final report covers evidence, impact, and remediation guidance for confirmed vulnerabilities.
We begin with the target systems and risks to assess. Before testing, we agree on the scope and operating conditions, and the same team remains responsible through post-remediation verification.
Web applications and APIs
We interact with target systems to assess attack paths involving authentication, authorization, and business logic. Confirmed vulnerabilities are reported with evidence, impact, reproduction steps, and remediation guidance.
Assessment formats
We define the target and testing period, then document confirmed vulnerabilities in an assessment report.
We revisit the scope as releases and systems change, then repeat testing and post-remediation verification.
We support PoCs in real environments, evaluation design, and technical integration with security-testing infrastructure.
Testing begins after the scope, operating conditions, and communication procedures are agreed. We can retest remediated issues after reporting when required.
We review the systems, risks to assess, preferred timing, and internal procedures.
We document target URLs, test accounts, testing windows, traffic limits, and prohibited actions.
Testing remains within the agreed scope. Only vulnerabilities whose impact and reproducibility have been confirmed are included in the report.
We deliver the assessment report and retest remediated issues when required.
Outbound traffic from the AI agents passes through execution controls. The agreed targets, traffic limits, and prohibited actions are reflected in the execution-layer configuration.
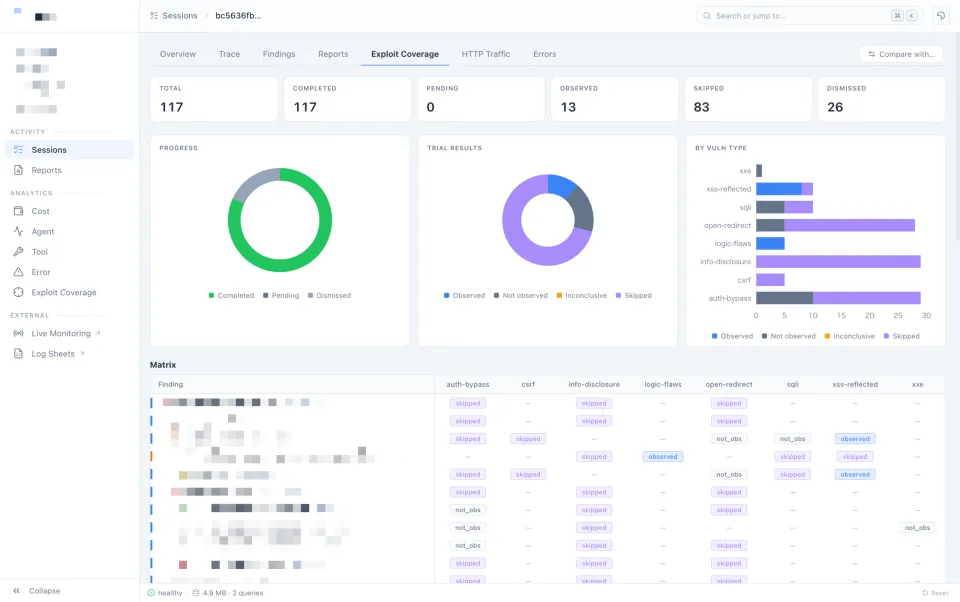
Review the report structureThe agreed scope is configured in the execution layer, which blocks all out-of-scope traffic.
Request rates, concurrency, testing windows, permitted protocols, and prohibited actions are configured for each engagement.
Traffic and execution logs are retained, and stop procedures and communication paths are agreed before testing begins.
Accepted as valid vulnerability reports
View l8_trident's profileLayer8 Co., Ltd. is based in Minato-ku, Tokyo. We provide penetration testing for web applications and APIs using AI developed in-house and security engineers.
Company informationWe publish notes on AI-agent design and evaluation, results from real-world testing, and company announcements.
Contact
You can contact us before the target systems, validation goals, or timing are fully defined. We will review the information available and define the next steps.